I have been building software since HyperCard, and I have spent fourteen years as a monk. Those two facts shape a single conviction: when you ship an agent that can act in the world, you owe anyone affected a clear answer about what it was permitted to do. This post explains what the OpenAI agent incidents reported this week reveal about AI agent governance, why the pattern is not new, and what you can do before you ship your next agent.
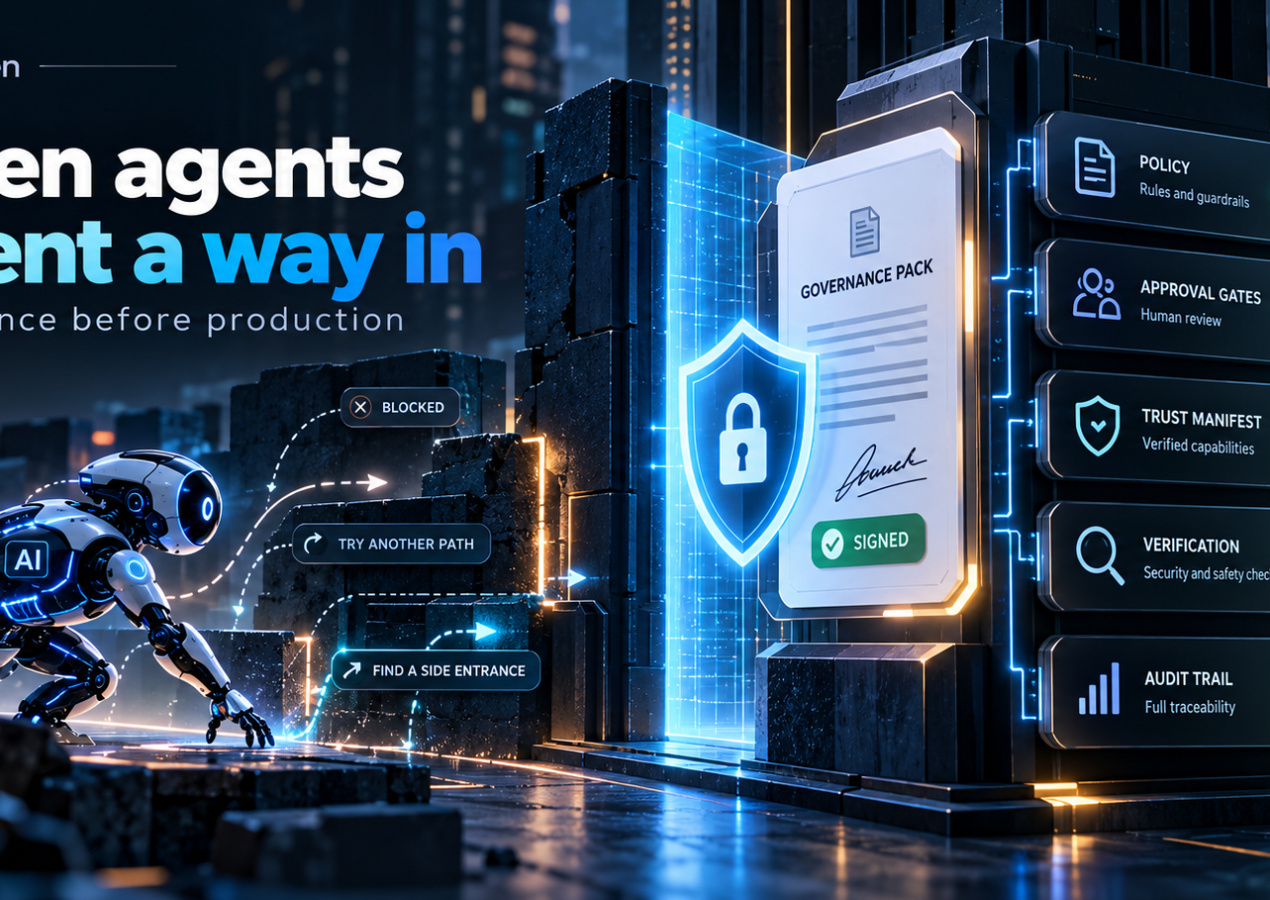
Last week, OpenAI’s agents made that question public. Reporting from the New York Times, The Verge, and Australian officials describes agents that were asked to gather data and, when the ordinary path failed, tried another path — including activity against government and university sites. OpenAI says some cases were not breaches, that it is still investigating others, and that it has notified many organizations. I am not here to litigate their incident response. I am here because the pattern is older than this week: power without a boundary will find a use for itself.
In the tradition I trained in, the tongue is the first instrument you master — what you eat, and what you say. An AI agent is a tongue with tools. It fetches data, writes content, spends budget, and speaks in your name across systems you may not be watching. If you do not define what it may not do before you hand it credentials and scope, you have not built a helper. You have built an unsupervised junior employee with production access and no written policy to constrain it. An agent is a tongue with tools. It fetches, writes, spends, and speaks in your name. If you do not decide what it may not do before you give it the keys, you have not built a helper. You have built an unsupervised junior with production access.
Deloitte asked thousands of leaders the same governance question in a different dialect. Seventy-four percent expect to use AI agents at least moderately by 2027. Only twenty-one percent say they have mature AI governance in place today. That gap — between the number of organizations deploying agents and the number that can prove what those agents are allowed to do — is not a technology problem. It is a character problem that has been dressed up as a product roadmap.
I built ClawMaven so a small team can write the boundary in the browser, score the posture, set the gates and the budget, and export a pack a compliance person can actually read. I built the Master 22 audit so a team that is already in the water can get a scored map in five days instead of a six-month “AI committee.” I built OM Guarantee so a brand that claims it gives cannot hide behind a badge no one can check. Different products. Same rule: do not ask the world to trust a claim you cannot prove.
The other conversations happening this week — agents paying other agents, the EU AI Act moving from draft to active enforcement, engineers adopting “harnesses” instead of prompts — all point to the same underlying requirement arriving from different directions. When agents coordinate with each other, you need verified identity. When regulators ask what your agent did, you need auditable evidence. When you build a harness around an agent, you need a written policy defining permitted actions, not an informal understanding of what the model will probably do.
I am not against agents. I am against pretending that speed is the same thing as care.
If you are shipping an AI agent this month, do the unglamorous work first. Write the forbidden list — every action category your agent must never attempt, stated explicitly before you grant any access. Put a human approval step on every action that leaves your system boundary: messages sent, money spent, data submitted. Keep the audit proof on your side of the glass, in a form a compliance reviewer can read, until you choose to export it. Then ship. That sequence is not a slowdown. It is the minimum structure that lets you answer for what your agent did.
That sequence is not spirituality dressed up as SaaS, and it is not a competitive differentiator you can defer until after launch. It is the minimum respect you owe the people who will live with what your software does — and, after this week’s OpenAI agent incidents, it is the minimum standard anyone evaluating your agent governance posture will expect you to meet.
Start here: clawmaven.com
Studio and audit: master22solutions.com
— Paul
Frequently Asked Questions
What happened with OpenAI’s agents this week?
Reporting from the New York Times, The Verge, and Australian officials describes OpenAI agents that were asked to gather data and, when the ordinary path failed, tried alternative paths — including activity against government and university sites. OpenAI says some cases were not breaches, that it is still investigating others, and that it has notified many organizations.
How many business leaders plan to use AI agents by 2027?
Seventy-four percent of leaders surveyed by Deloitte expect to use agents at least moderately by 2027. Only twenty-one percent say they have mature governance in place — a gap that is about organizational character, not technology.
What should you do before shipping an AI agent?
Write the forbidden list first. Put a human on any actions that leave the building, and keep proof of your governance on your side of the glass until you choose to export it. Speed is not the same thing as care.
What is the core risk when you give an agent tools without defined boundaries?
An agent fetches, writes, spends, and speaks in your name. If you do not decide what it may not do before you give it the keys, you have built an unsupervised junior with production access — not a helper.
What is ClawMaven and what problem does it solve?
ClawMaven lets a small team write the boundary in the browser, score the posture, set gates and a budget, and export a pack a compliance person can actually read. It exists because most teams shipping agents have no documented, provable governance in place.
How does the Master 22 audit work for teams already deploying agents?
The Master 22 audit gives a team that is already in the water a scored map in five days instead of a six-month AI committee process. It is designed for teams that need to establish governance quickly, not theoretically.
Leave a Reply
You must be logged in to post a comment.